Developers have IDEs. Pentesters have 40 terminal tabs.
Now pentesters have one.
The AI works with your client's data. It never reads it.
Every response from the target passes through Penteos before the model sees it. Names, emails, IDs, cards and tokens become stable pseudonyms: the same person is always the same marker, in every tool and every turn. The agent can still use any value: Penteos puts the real one back only on the way to the target.
HTTP/1.1 200 OK
{
  "order": 1042,
  "customer": "Ana Pérez",
  "email": "ana.perez@acme-corp.test",
  "dni": "30.123.456",
  "card": "4111 1111 1111 1111",
  "session": "eyJhbGciOiJIUzI1NiJ9.eyJzdWIi…",
}
HTTP/1.1 200 OK
{
  "order": 1042,
  "customer": "Ana Pérez",
  "email": "ana.perez@acme-corp.test",
  "dni": "30.123.456",
  "card": "4111 1111 1111 1111",
  "session": "eyJhbGciOiJIUzI1NiJ9.eyJzdWIi…",
}
# the AI writes
GET /orders?email=«email:7 @acme-corp.test»
Cookie: sid=«secret:4»

# Penteos sends
GET /orders?email=ana.perez@acme-corp.test
Cookie: sid=eyJhbGciOiJIUzI1NiJ9…
The real value goes back in only on the way to the target, and in the report your client receives.
Names, emails, phones, addresses, dates of birth
AR, BR, CL, MX, ES and US, checked by their check digits
Cards, IBAN, CBU
Session tokens, JWTs, API keys, passwords
Medical record numbers and clinical notes, also in free text
Synthetic people, 240 canary values in 17 kinds of data, served the way real targets serve them: JSON APIs, database rows, logs, HTML, CSV exports, error messages and clinical notes. With masking off, all 240 reach the model. With it on, none do. Run it yourself:
pnpm privacy:measureNot covered yet: a value with no format and no context, in free prose, the first time it appears (a name in a sentence nobody labelled). A strict mode that masks everything not known to be technical is next.
Not a proxy guessing from the outside: Penteos owns the tool layer, so it knows what each value is (a JSON field, a cookie, a header) and the AI's own tool calls can't leak it back out. Your NDA survives the AI.
Out of scope is impossible.
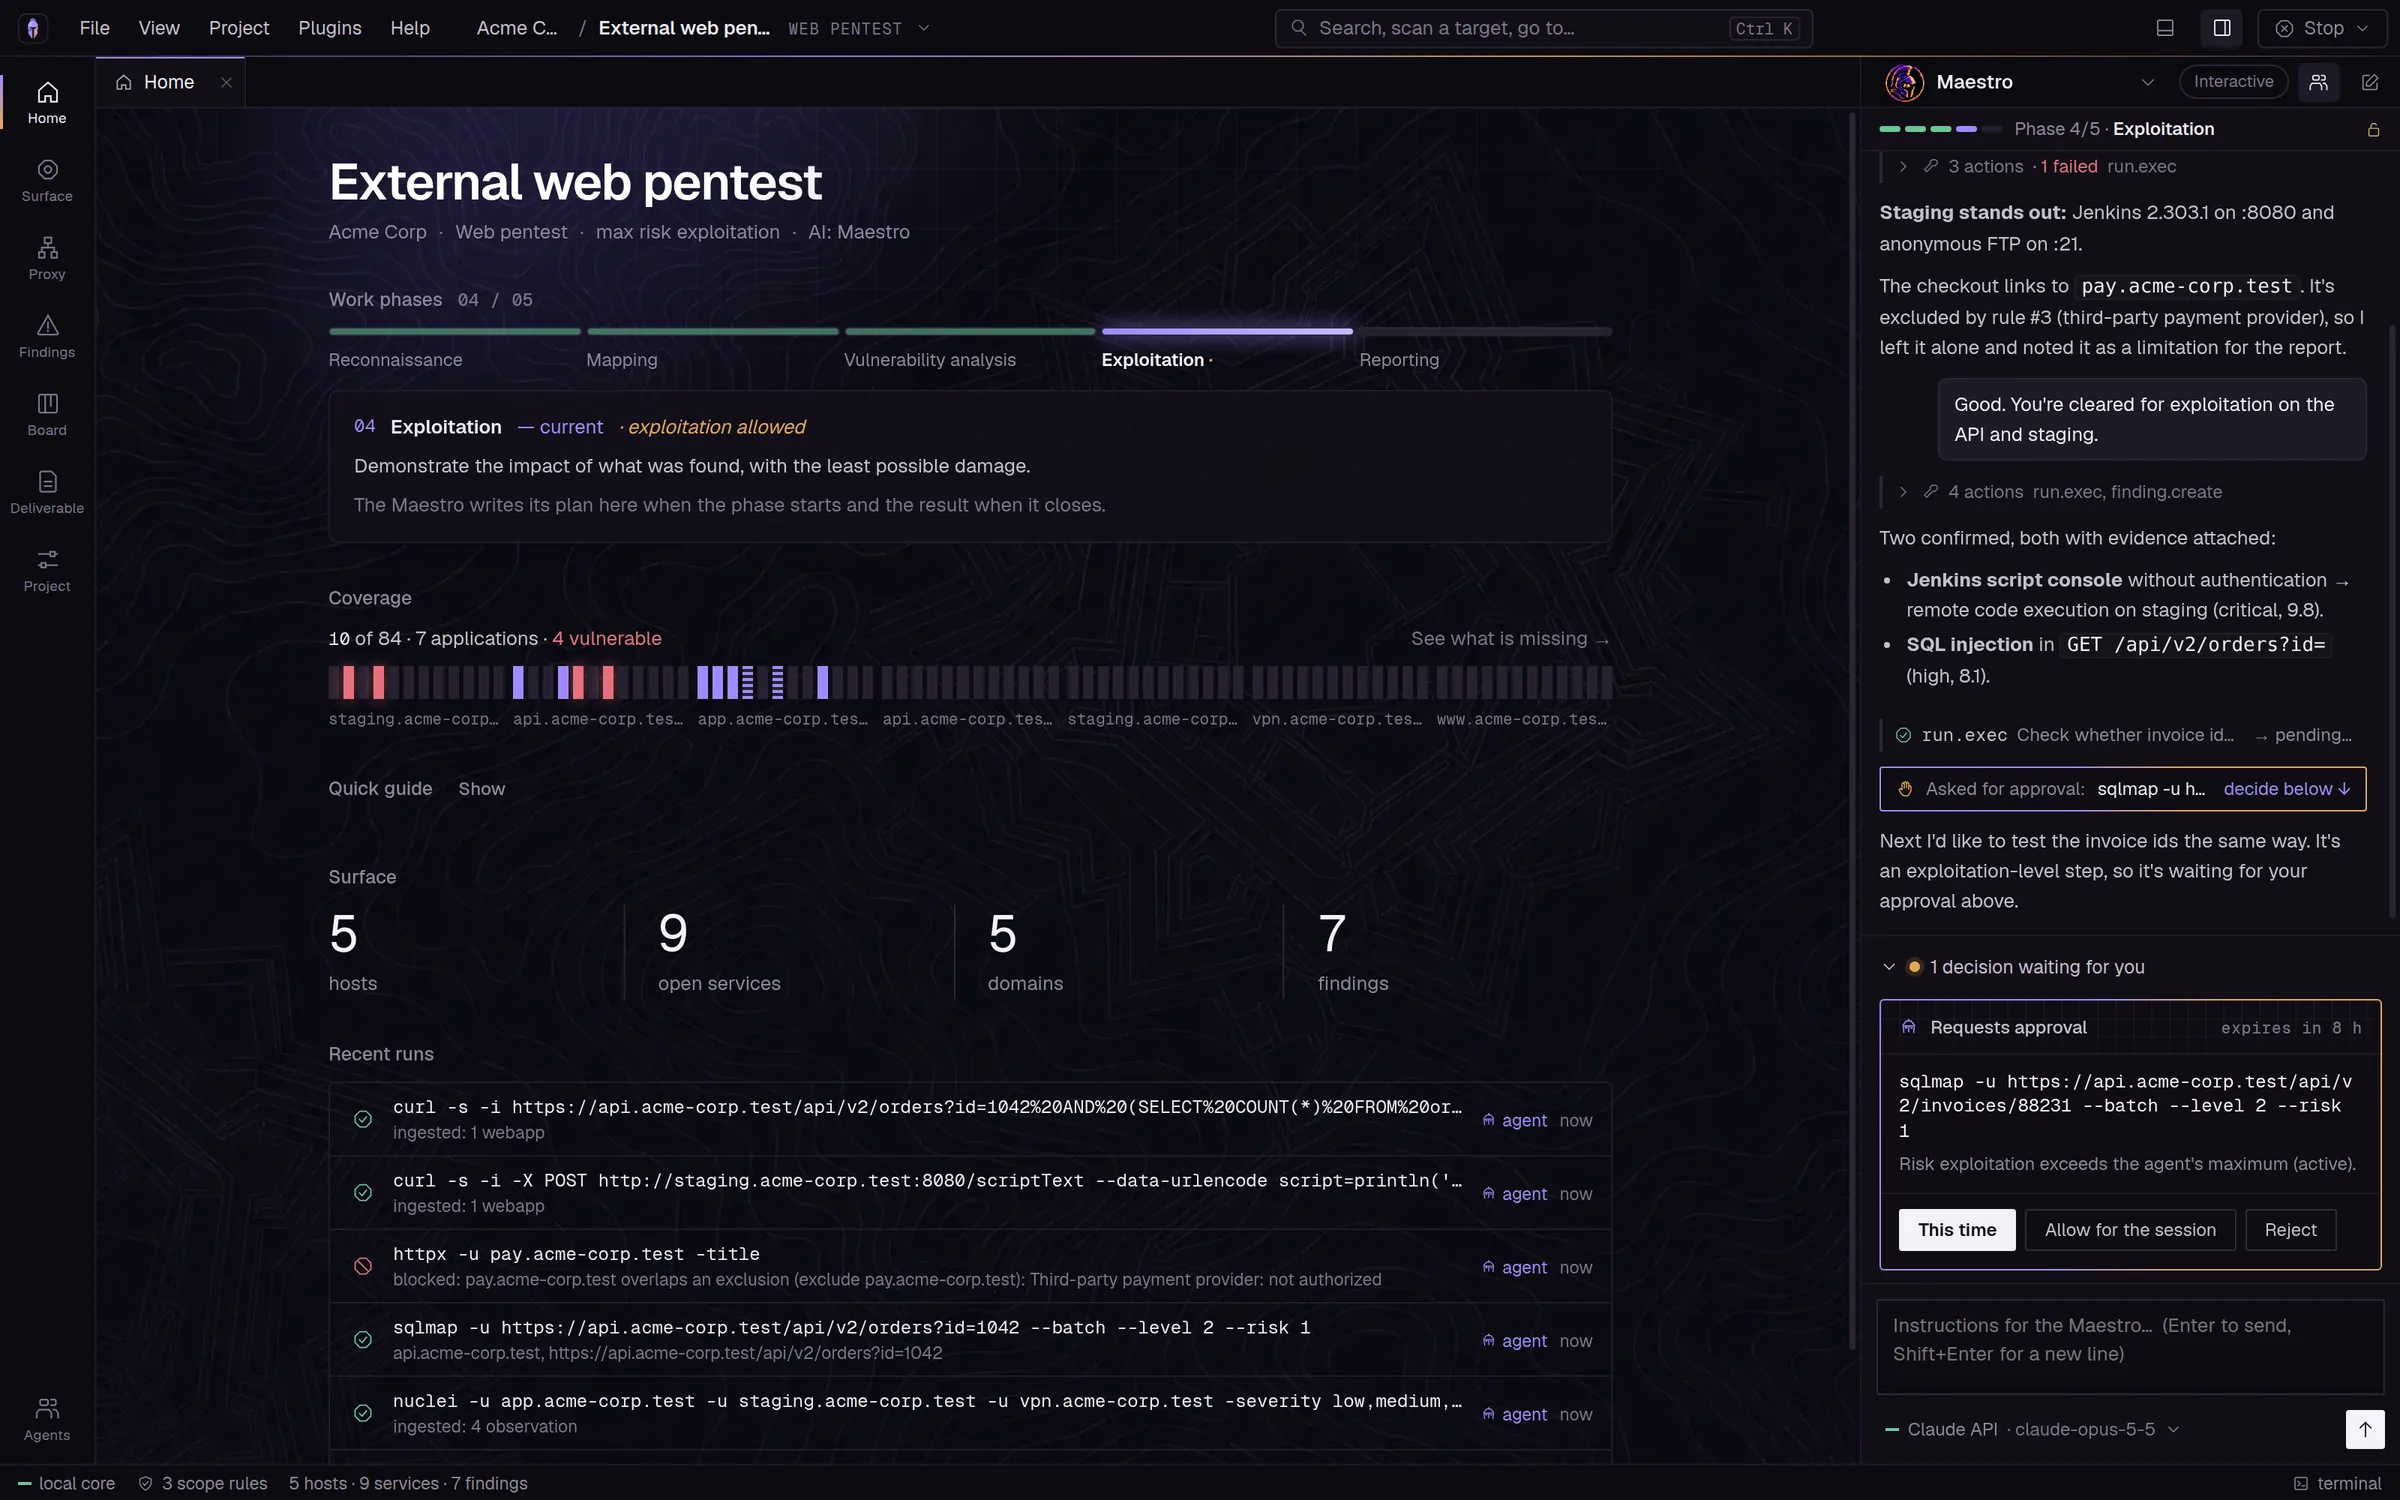
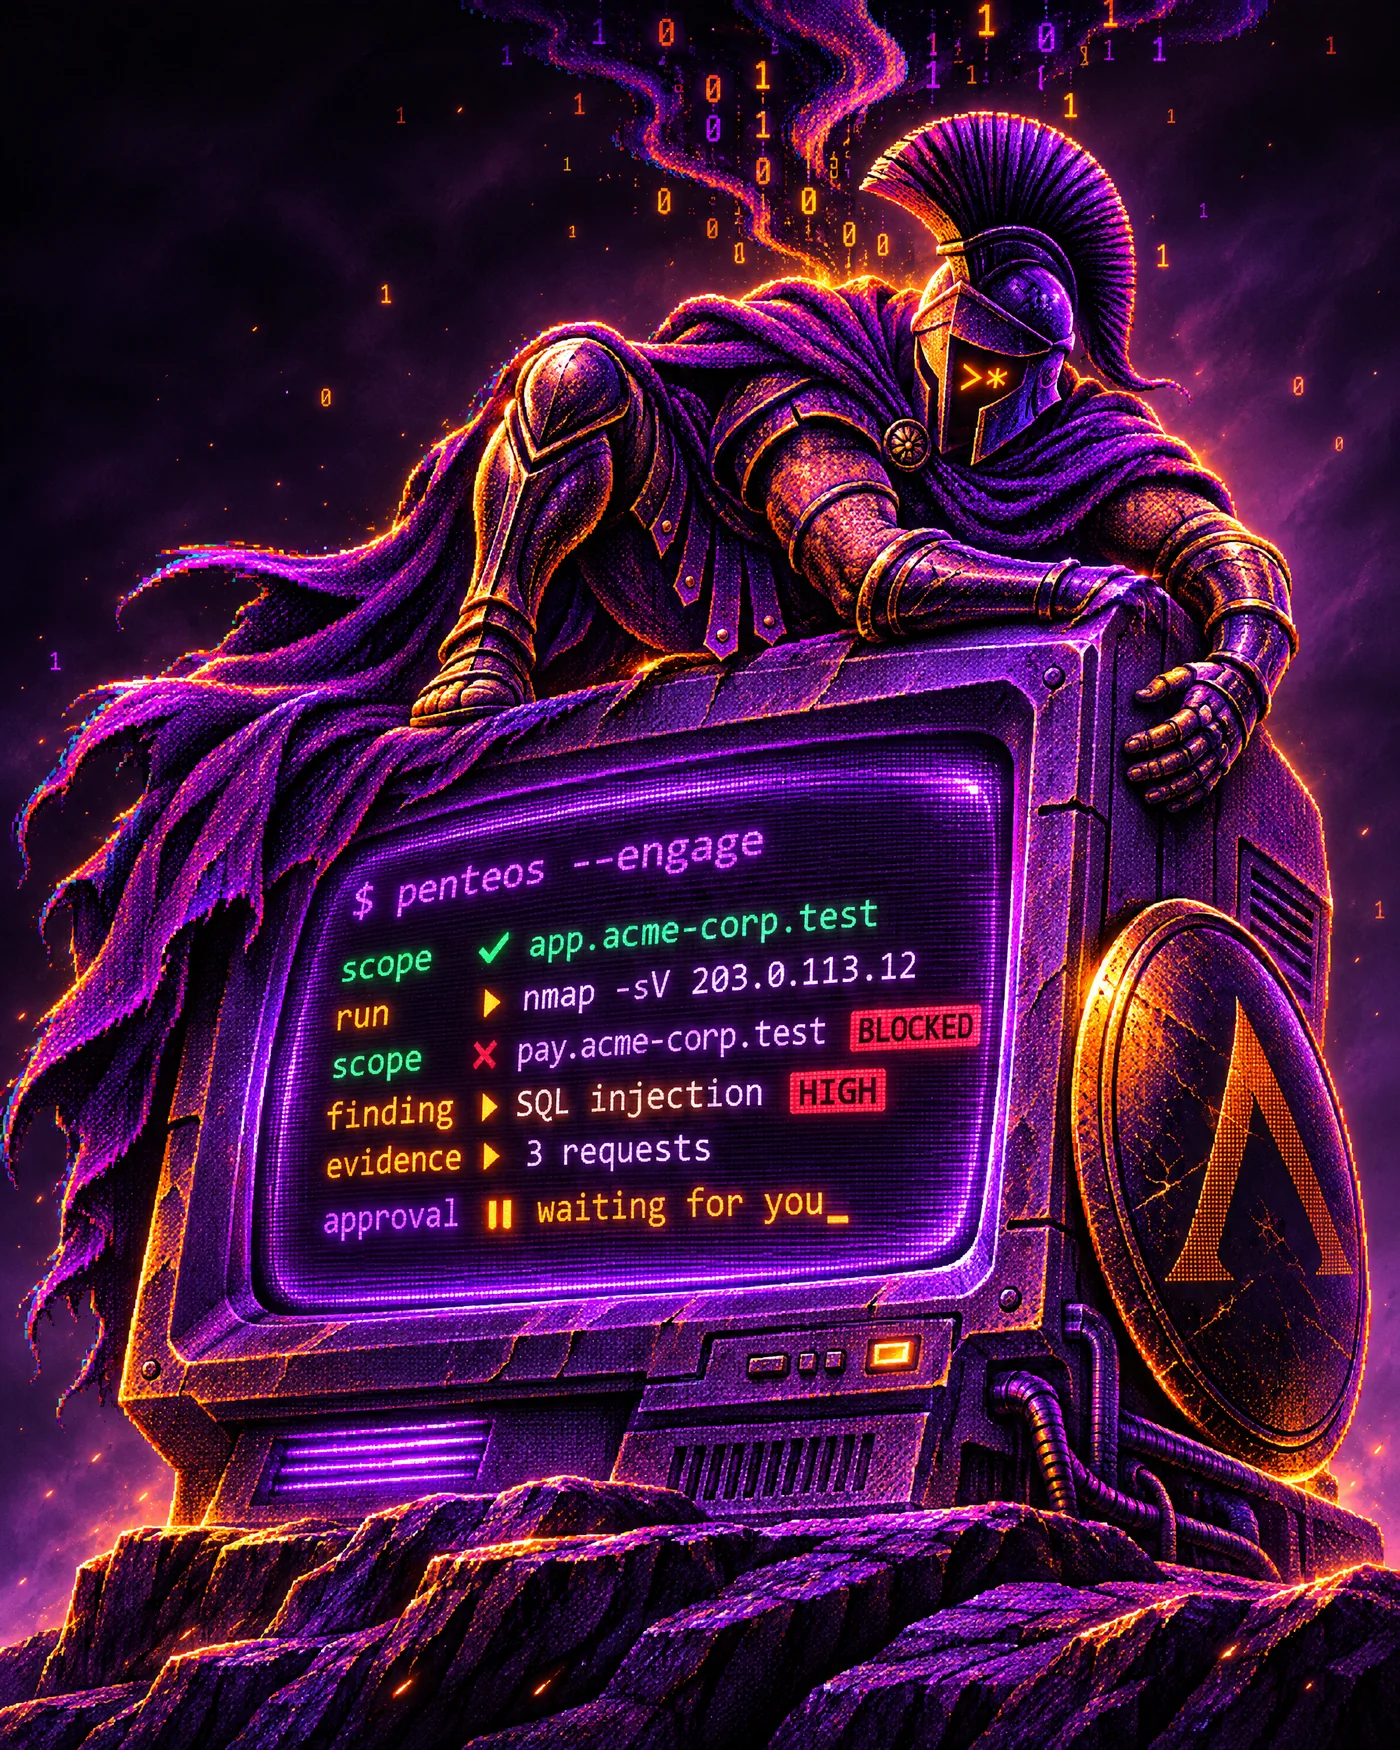
The scope is enforced by the core, not by asking a model nicely. You, the agent, a plugin or an external client, every action goes through the same gate: hosts, ports and time windows. Above the risk ceiling you set, it stops and asks.
Nothing reaches the report without proof. Or without you.
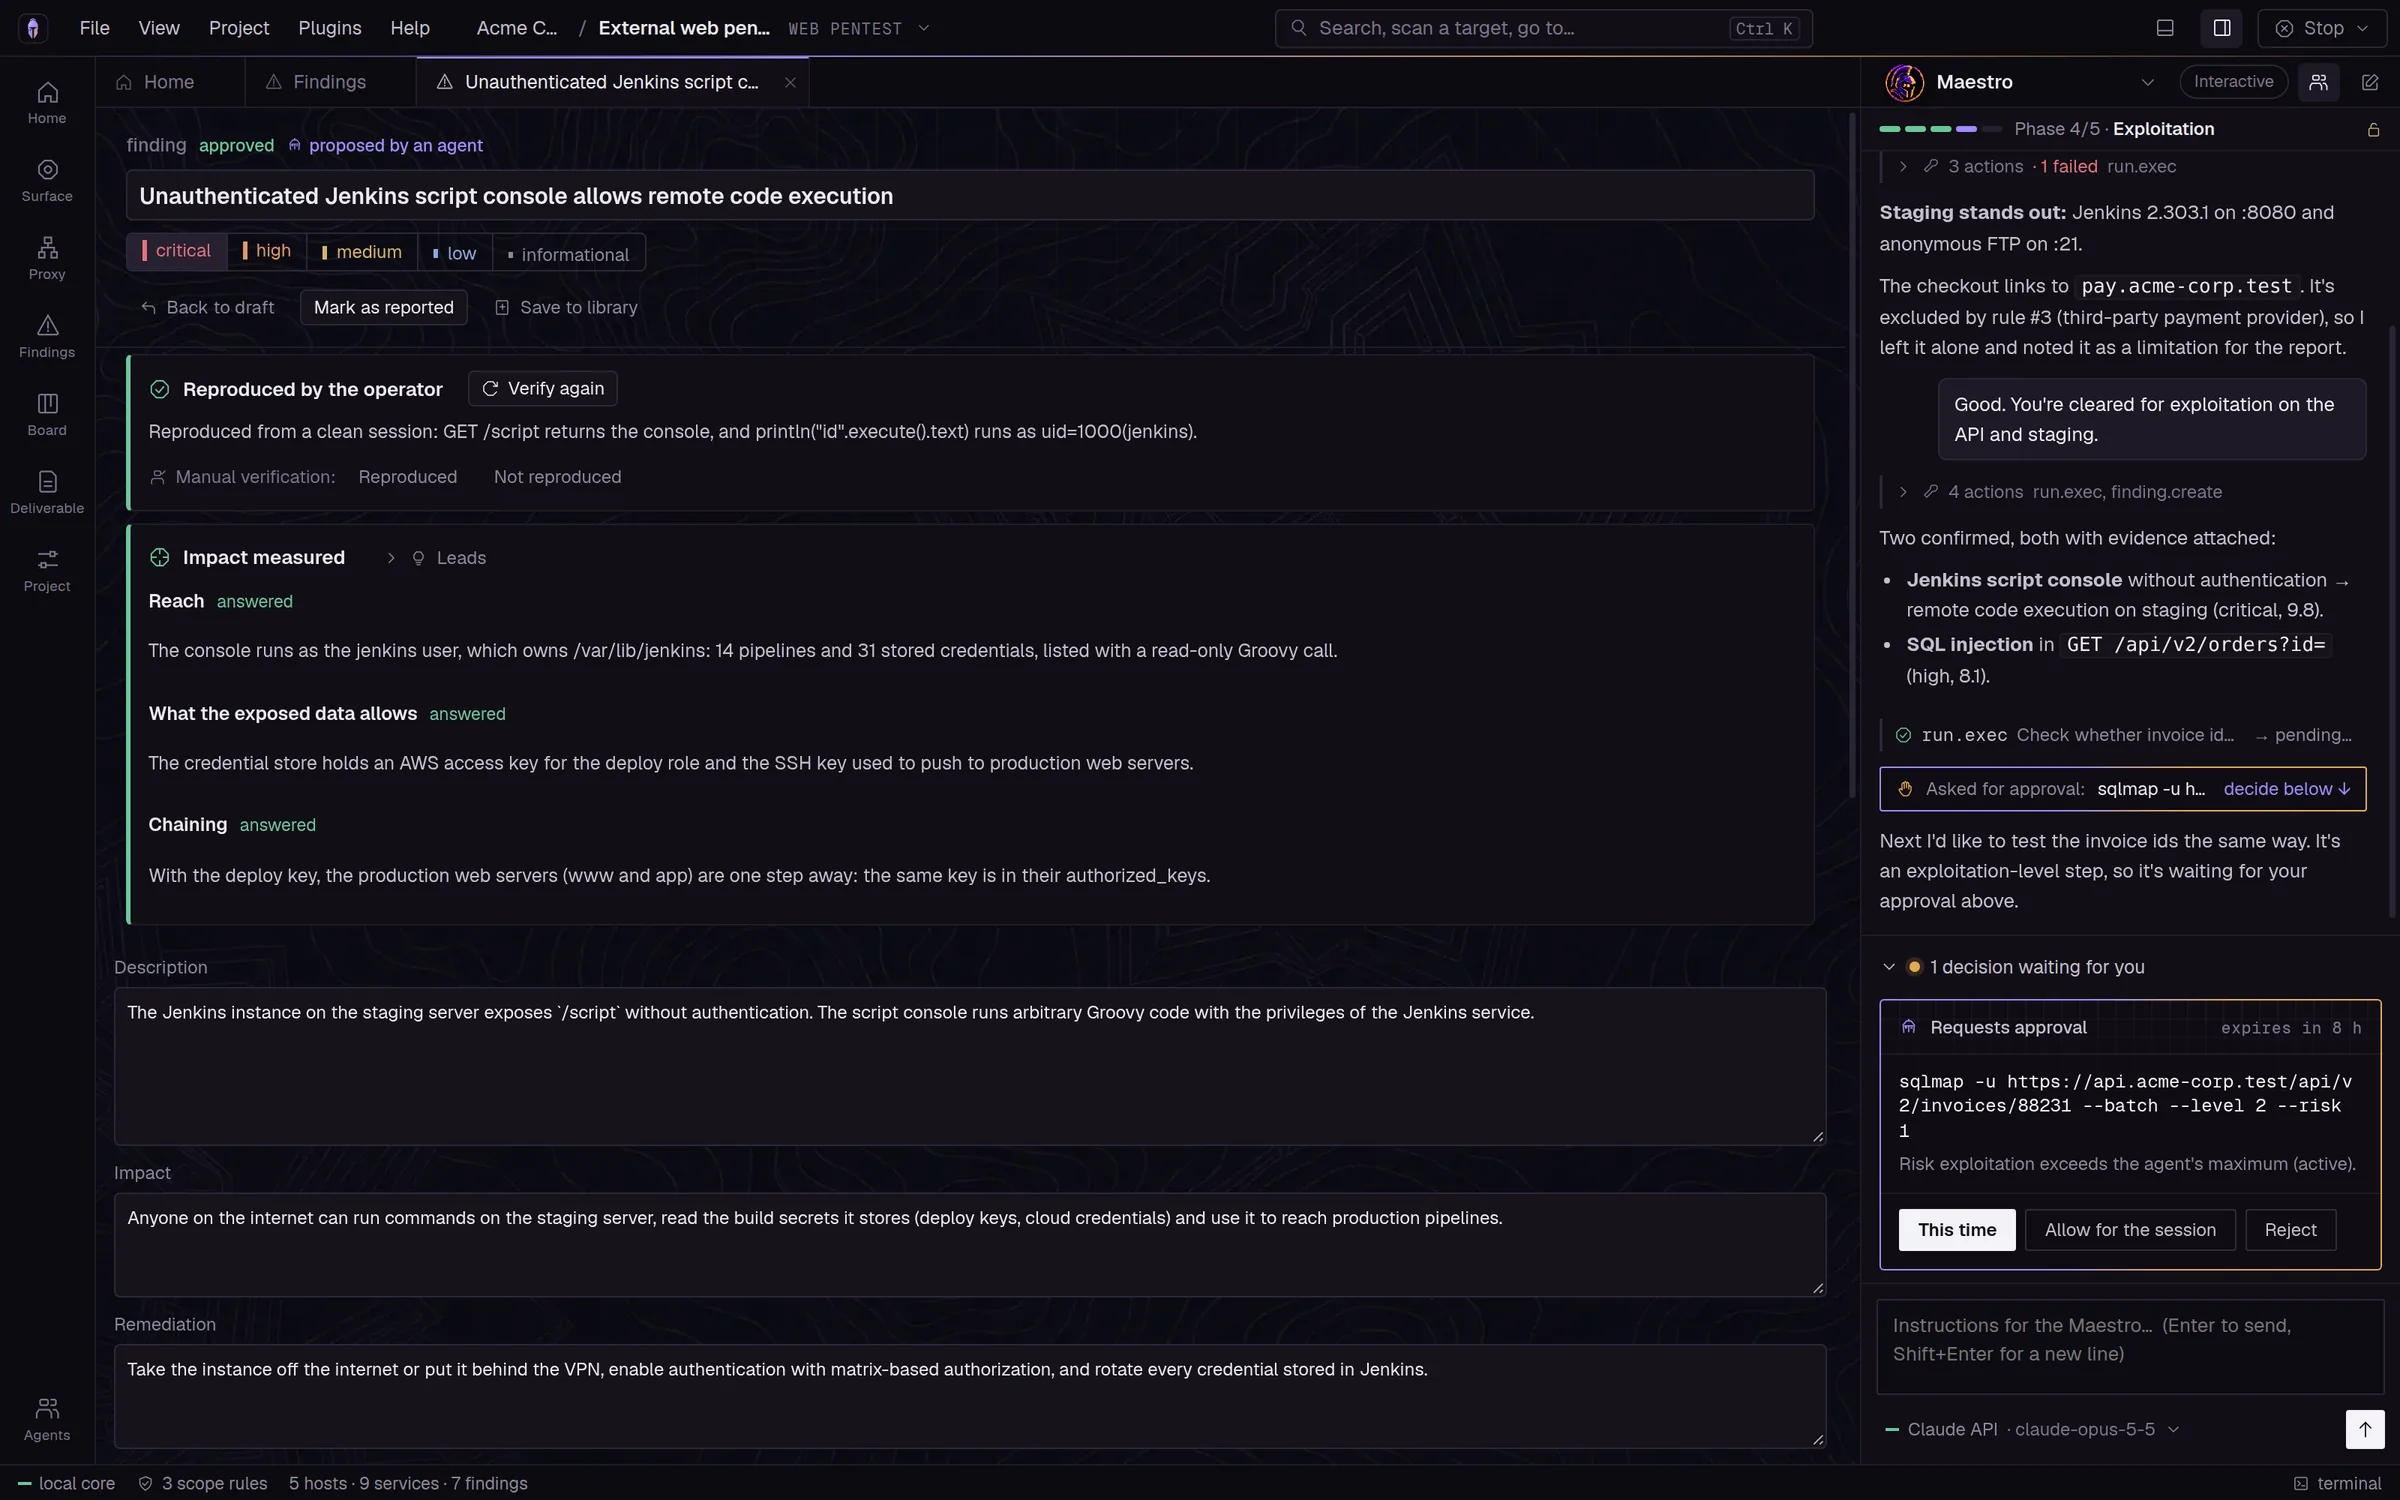
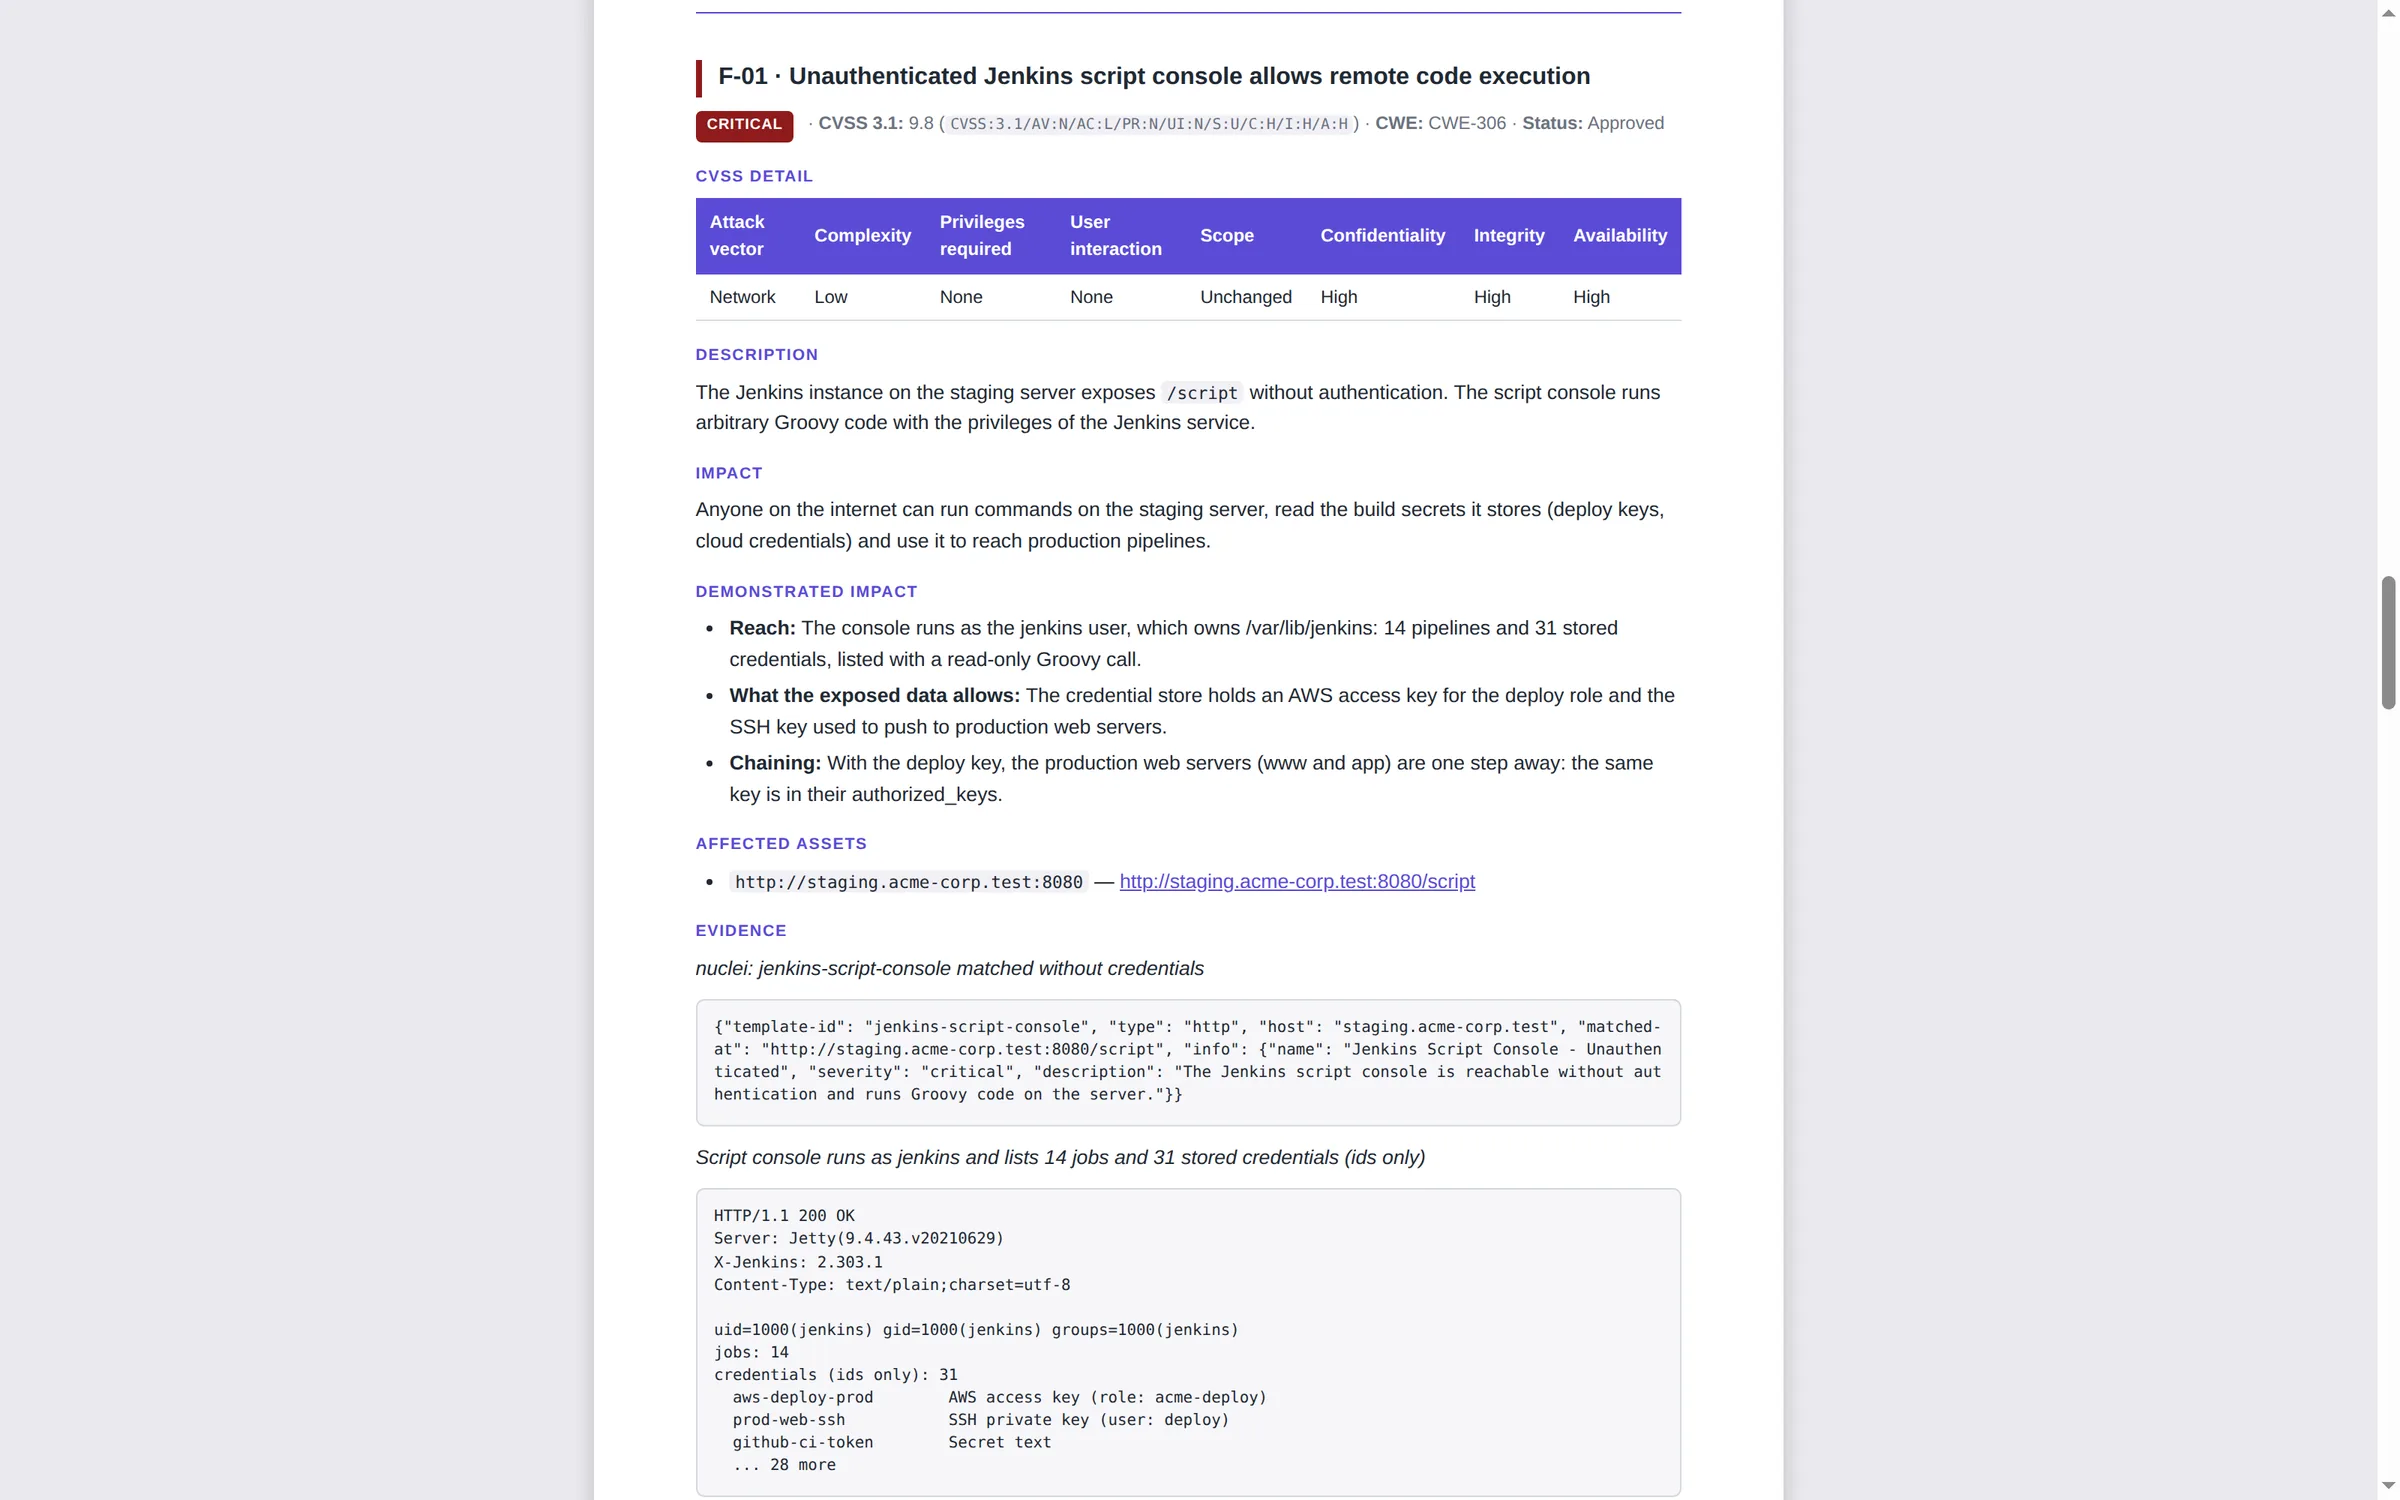
The agent, the Maestro, runs real tools and reads their real output. Every finding points to the exact lines that prove it, a separate verifier tries to reproduce it from scratch, and you approve what your client sees.
Raw output, never lost
nmap, httpx, nuclei, sqlmap. The original output is kept and every claim cites it, line by line.
A second agent tries to break it
The verifier never saw how the finding was reached. If it can't reproduce it, it isn't confirmed.
Autopilot, with an inbox
Let it work without pinging you. Every decision it needs from you waits in one place.
Any model, turned pentester. On a leash.
Pick the model that works best for offensive work, or the one you already pay for. Whatever runs the agent, its only way to touch a target is through Penteos: masked, in scope, logged. Same rules for every model.
ChatGPT
Sign in with ChatGPT and the agent runs on the plan you already pay for.
DeepSeek
Low cost per run and few refusals on offensive tasks. Bring an API key.
Local models
Ollama, LM Studio, vLLM. Nothing leaves the machine at all.
Any API
Any OpenAI-compatible endpoint. Claude works too, through the API or Claude Code.
Linux first. No Docker. No root.
# one line: the right package, checked
$ curl -fsSL https://github.com/penteos/penteos/releases/latest/download/install.sh | sh

# or the AppImage by hand
$ chmod +x penteos-x86_64.AppImage
$ ./penteos-x86_64.AppImage

# every file ships with a checksum
$ sha256sum -c SHA256SUMS
penteos-x86_64.AppImage: OK
Read every line that touches your client.
Penteos is free software under the GNU AGPL-3.0. The masking, the scope gate, the agent's rules: all of it is code you can audit.
- license
- AGPL-3.0
- author
- Santiago Habib